Introduction: The Illusion of Safety in Visual Development Ecosystems
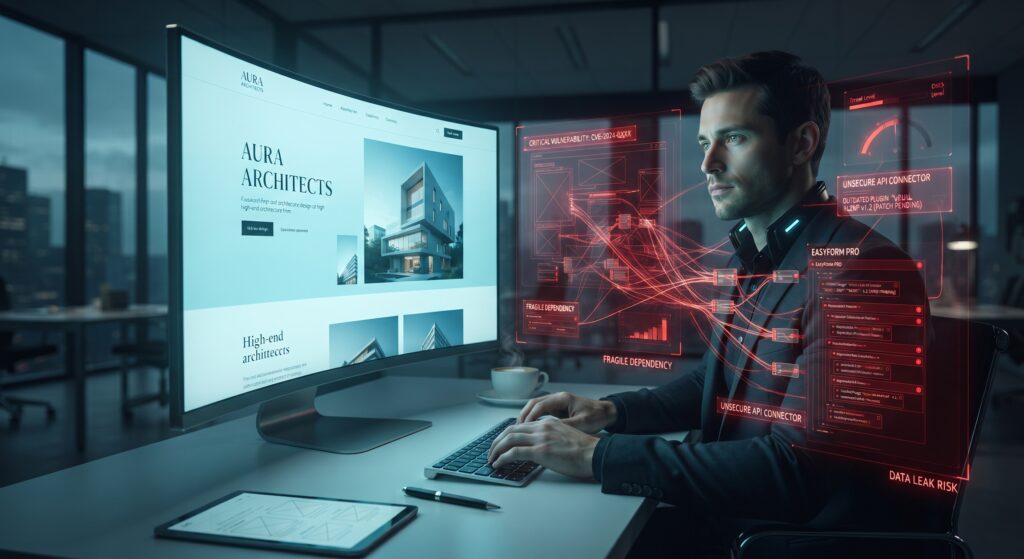
The Rapid Rise of Visual Environments via No-Code Extensions
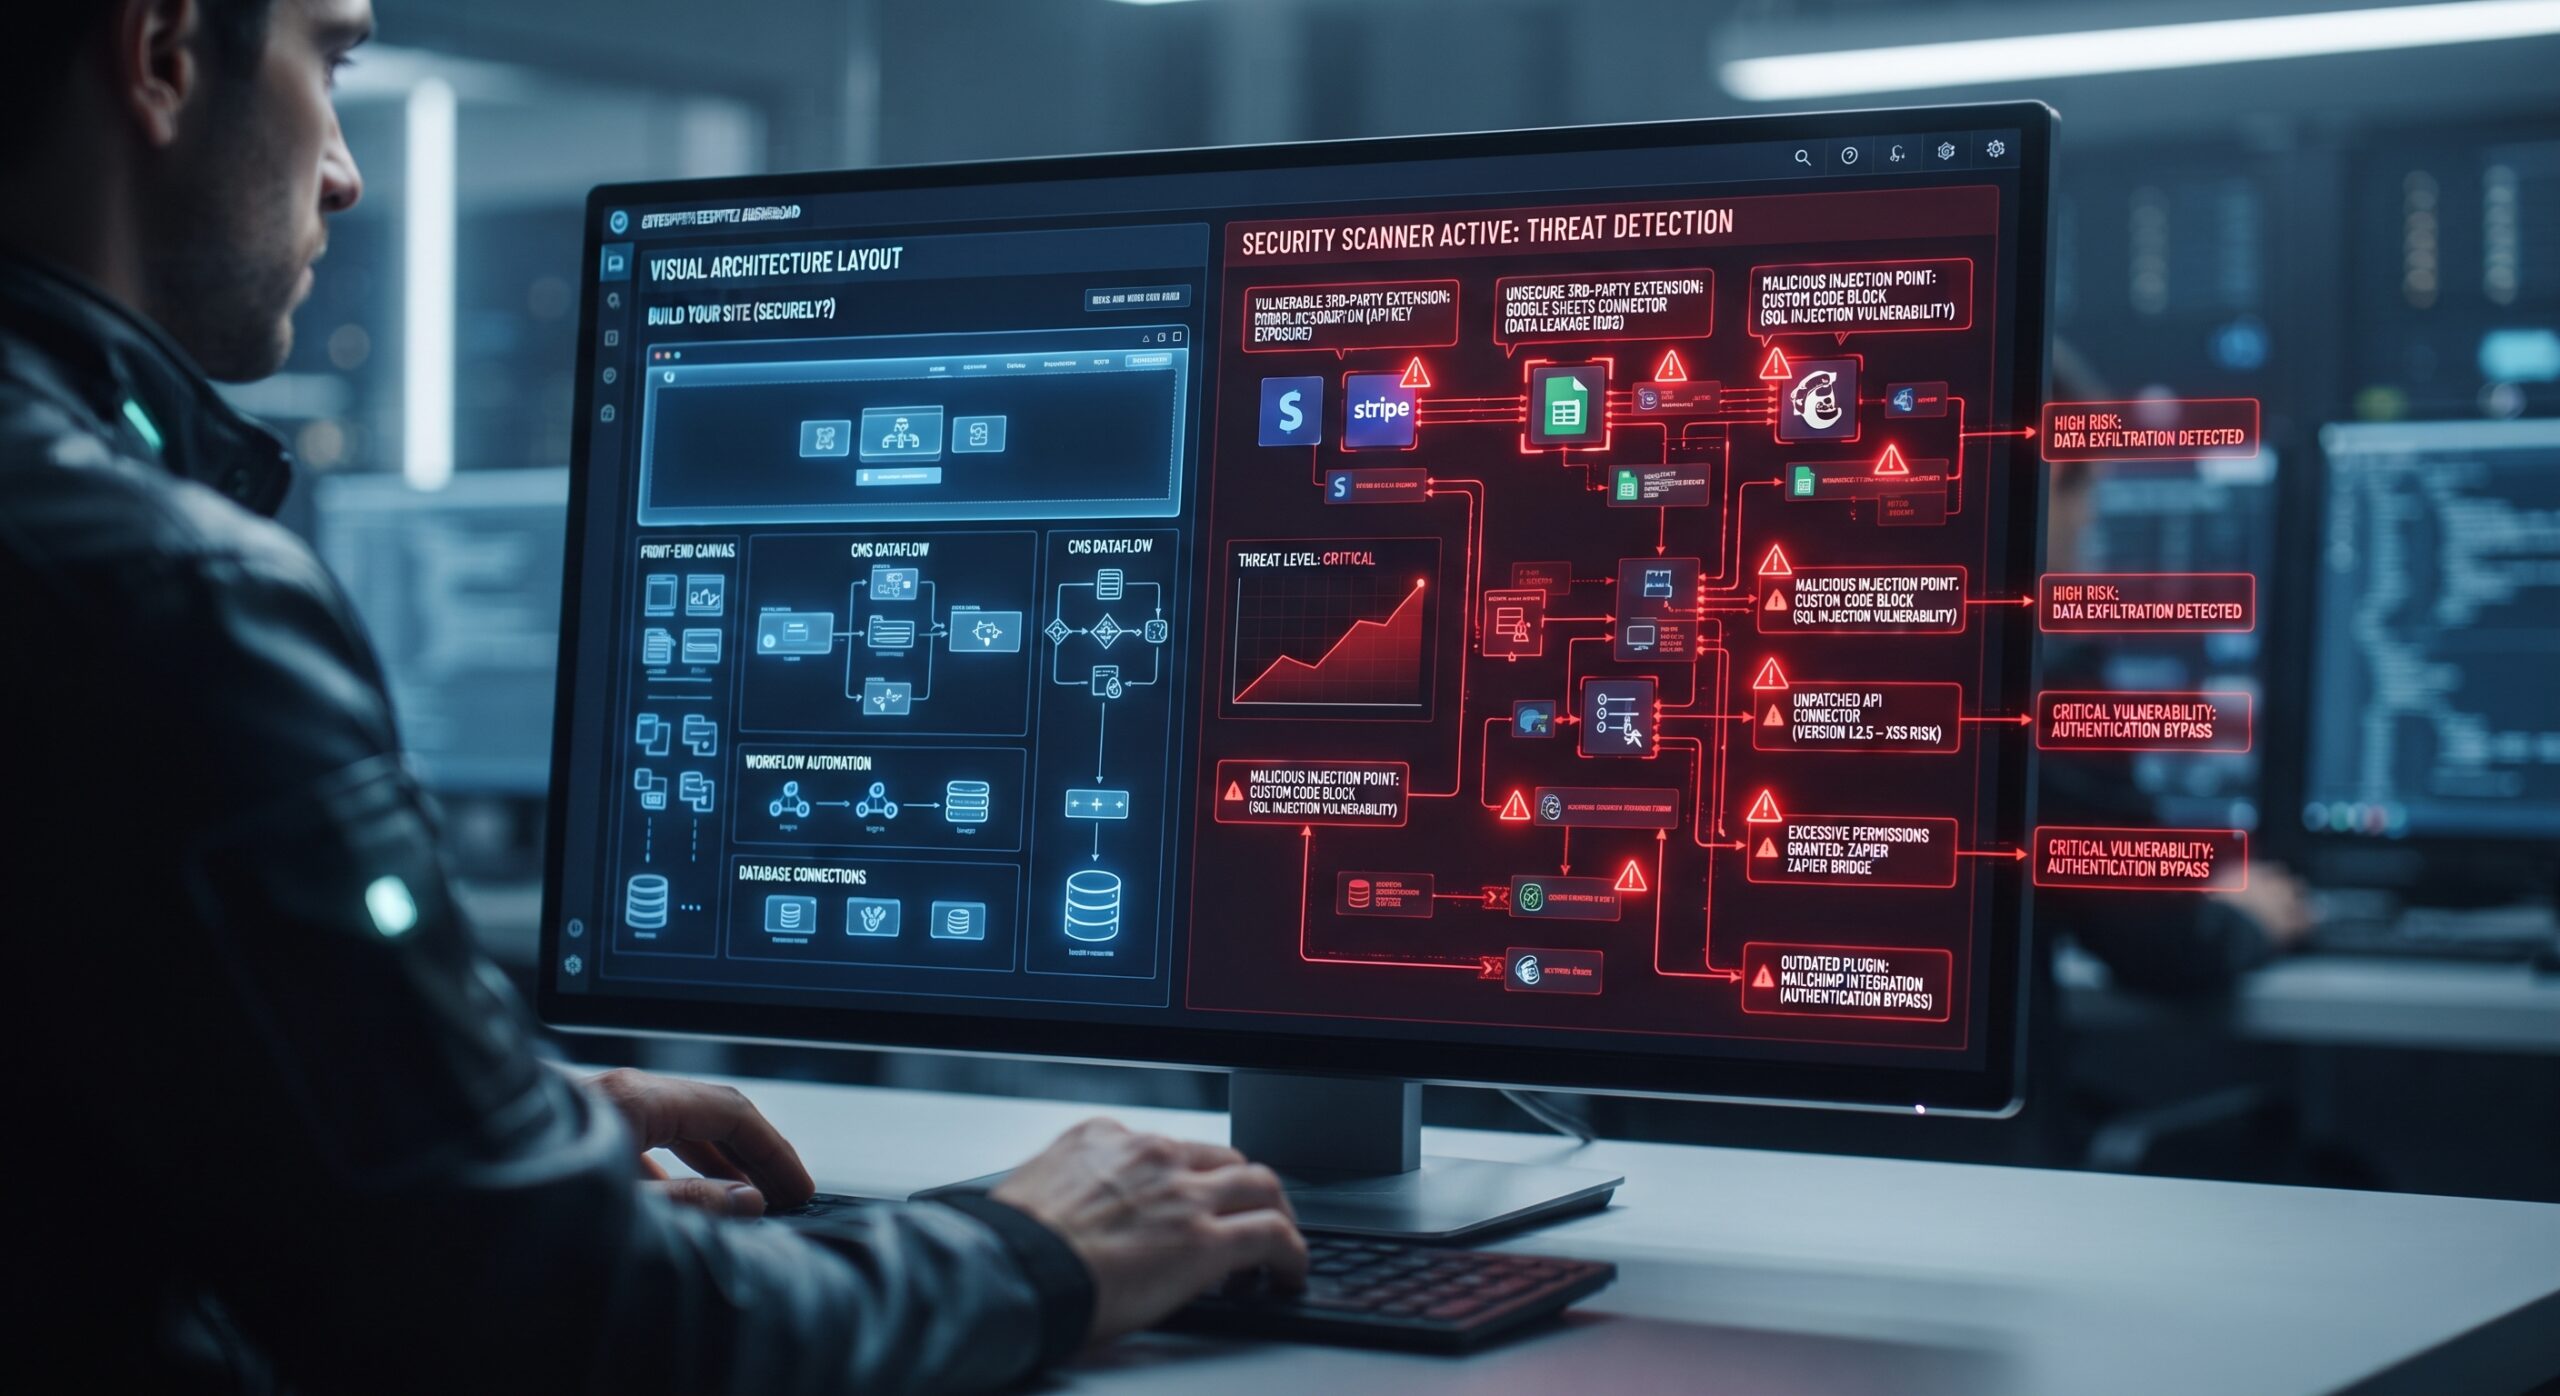
The software development landscape has shifted dramatically, with startups and enterprises alike embracing platforms like Webflow, Wix Studio, and WordPress powered by no-code extensions to accelerate digital delivery. These visual environments allow teams to launch fully functional web apps and corporate sites in days rather than months. However, this unprecedented speed often creates a dangerous psychological illusion: the assumption that infrastructure-level safety equals complete application security.
Platform Security Versus Application Vulnerabilities
While major platform vendors manage hosting security, SSL configurations, and core uptime, they do not control how third-party plugins, widgets, and custom scripts handle data. Consequently, the responsibility of maintaining a secure architecture falls squarely on the creators. When development teams integrate external modules without rigorous code audits, they introduce deep security blind spots directly into production systems.
Shifting Focus to the Real Threat Vector
Security breaches in modern web architectures rarely occur because the underlying cloud infrastructure failed. Instead, attackers target the fragile connective tissue—the third-party no-code extensions, API bridges, and form handlers—that power everyday site functionality. Understanding these risks is critical for engineering teams aiming to build resilient digital assets.
Common Security Vulnerabilities Handled by No-Code Extensions
Unvetted Code and Abandoned Repositories
The vast marketplaces of WordPress plugins, Wix app markets, and Webflow community components contain thousands of add-ons built by independent developers. Many of these packages lack active maintenance, leaving unpatched CVE records open for exploitation. When an outdated plugin features a backdoor, malicious actors can easily leverage it to inject malware, deface pages, or hijack admin controls.
Loose Access Controls and Client-Side Logic Flaws
Many visual builders rely heavily on client-side permission checks rather than strict server-enforced rules. For instance, if a no-code extension hides administrative UI elements based solely on front-end conditional visibility, sophisticated users can manipulate browser tools or API endpoints to bypass restrictions. This structural flaw opens paths to unauthorized data modification and privilege escalation.
Unsanitized Form Inputs and Injection Vectors
Modules that handle user input—such as feedback forms, dynamic calculators, or login portals—frequently fail to sanitize data properly. If a third-party script provided by no-code extensions passes raw strings directly into database queries or DOM elements, systems become instantly vulnerable to SQL injection and cross-site scripting (XSS) attacks.
Data Exposure Risks via Loose API Connectors and Webhooks
The Danger of Exposed API Keys
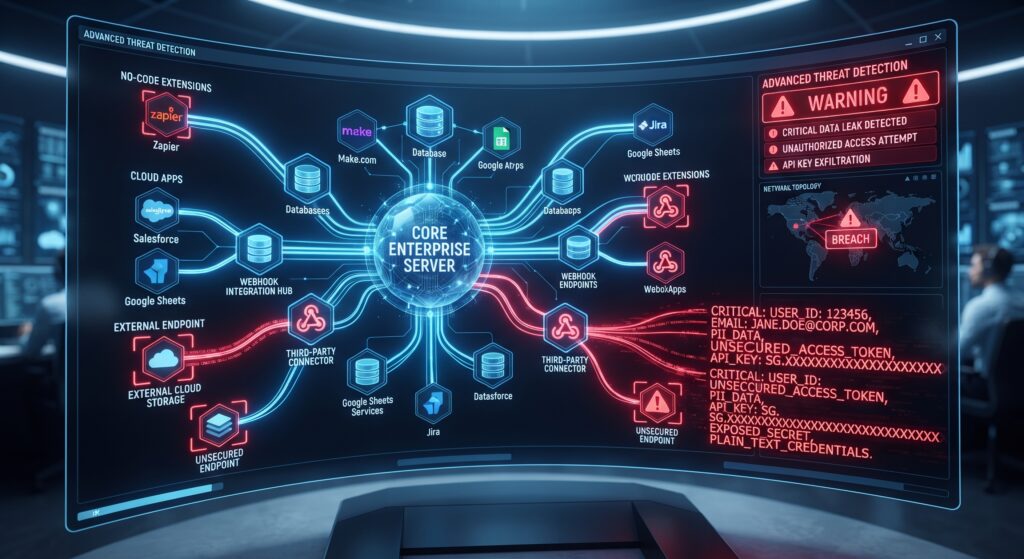
No-code workflows thrive on connectivity, using webhooks and API tokens to sync data with external CRM platforms, payment gateways, and databases. However, developers often misconfigure these connectors when setting up various no-code extensions, exposing secret API keys within client-side JavaScript code. Once exposed in browser inspect tools, these credentials allow attackers to extract or manipulate backend databases.
Publicly Accessible Data Views
A recurring vulnerability across modular web stacks involves misconfigured privacy permissions on data views managed by external tools. Relying on obscure URLs or hidden UI lists to protect sensitive user information fails because automated crawlers or network sniffers can index these endpoints. Ensuring strict, token-authenticated data fetching is essential to prevent unexpected data leaks.
Comparative Matrix: Native Security Versus No-Code Extensions Risk
Architectural Control and Attack Surface
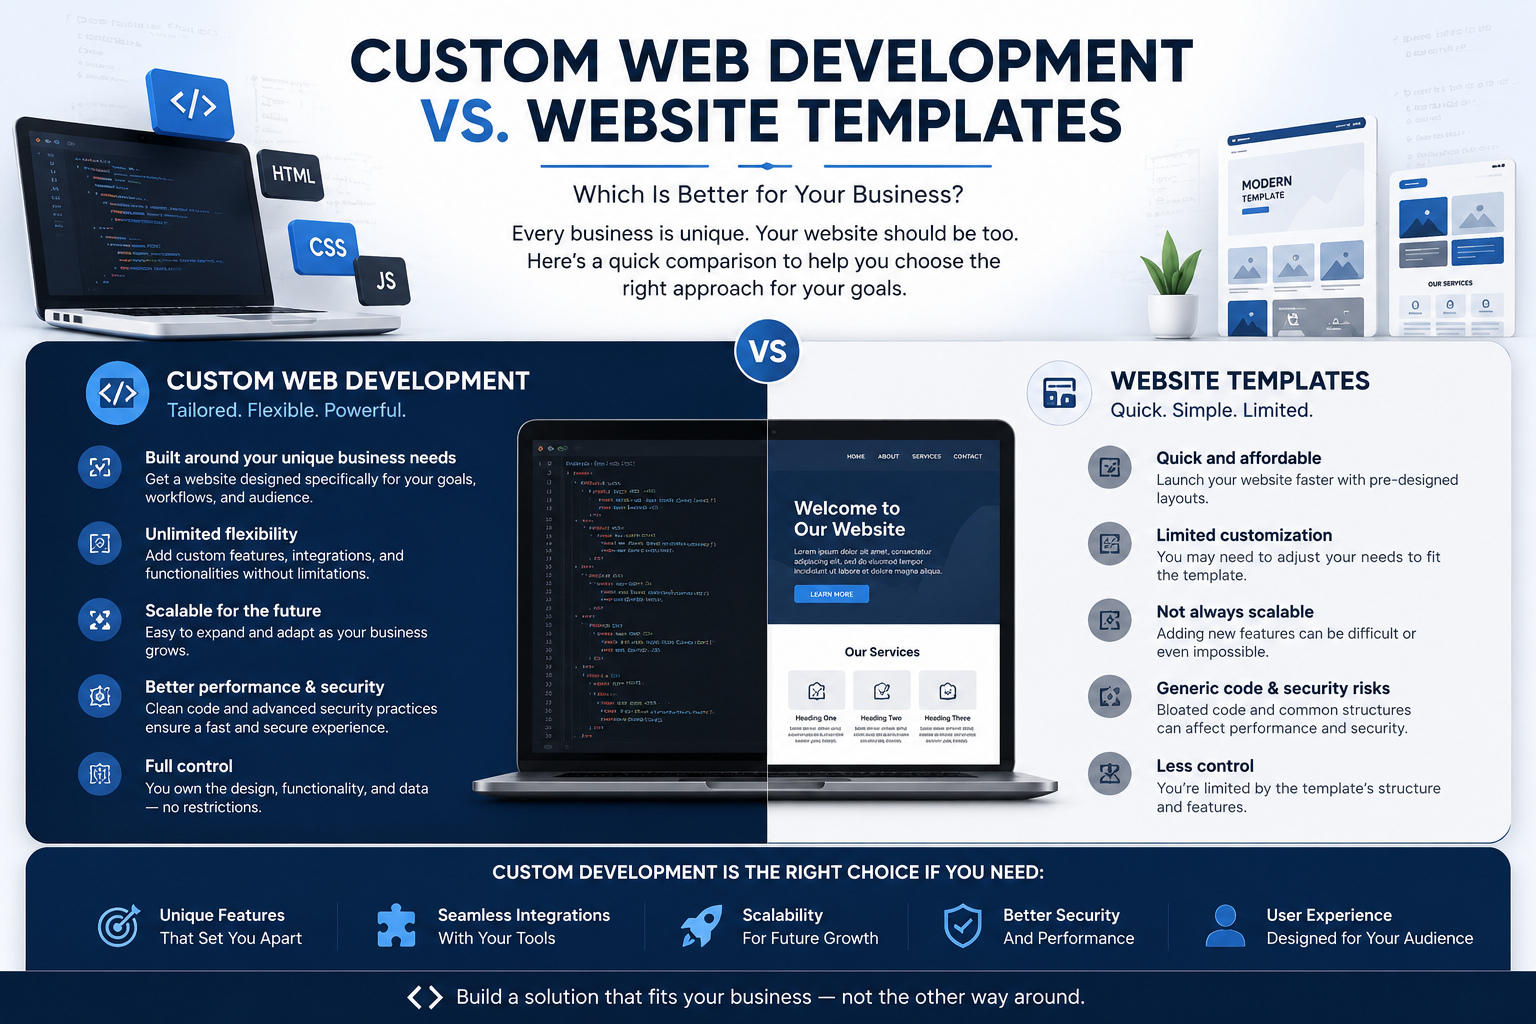
Relying strictly on native platform code minimizes the overall attack surface because core features undergo rigorous internal testing. Conversely, adding dozens of third-party no-code extensions exponentially expands the threat landscape, as every added module acts as a potential entry point for attackers.
Maintenance Overhead Versus Speed
While third-party add-ons provide instant features, they introduce severe long-term maintenance overhead. When a core platform updates its framework, unoptimized plugins often break or expose security flaws, forcing engineering teams into reactive firefighting rather than proactive feature development.
Best Practices for Hardening No-Code and Low-Code Environments
Implementing Strict Extension Audits for No-Code Extensions
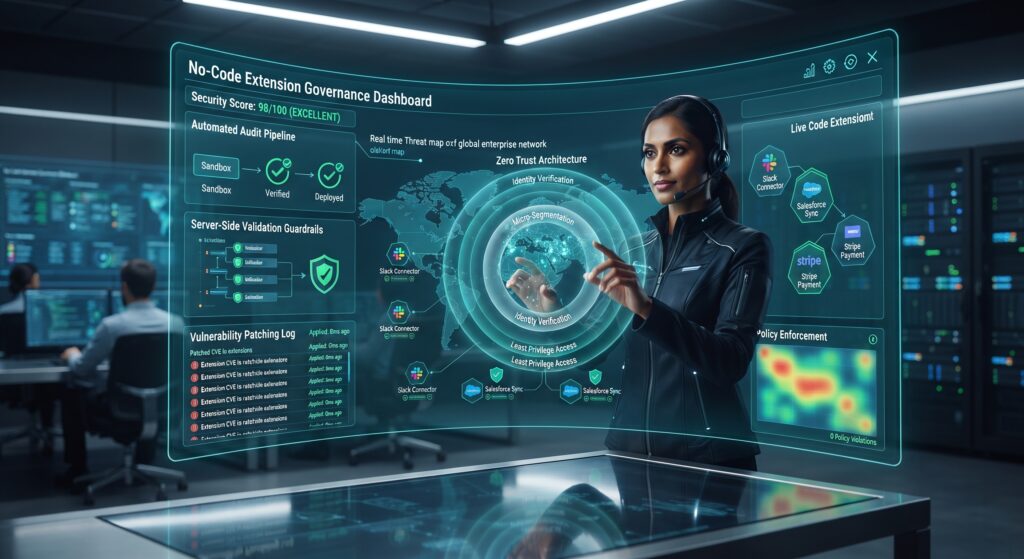
Organizations must establish a centralized vetting process before installing any third-party no-code extension. Teams should review update frequencies, developer reputations, and permission requirements to ensure the add-on complies with enterprise security standards.
Enforcing Server-Side Validation and Zero-Trust Principles
Never trust client-side restrictions. Ensure all data processing, permission checks, and input sanitization routines occur securely on the server side. Adopting a zero-trust architecture ensures that every data request undergoes strict verification, safeguarding the application against unauthorized access.
Frequently Asked Questions (FAQs)
Q1: What are the main security risks of using third-party no-code extensions?
Third-party add-ons often lack rigorous maintenance, leaving unpatched vulnerabilities, loose access controls, and unsanitized input fields that malicious actors can exploit to breach application data.
Q2: Do platforms like Webflow or WordPress take care of all security requirements?
Platform vendors handle core infrastructure security, hosting safeguards, and SSL certificates, but they do not manage the custom code, scripts, or installed no-code extensions.
Q3: How do exposed API keys compromise low-code web applications?
If API keys or webhooks connected through no-code extensions are improperly embedded into client-side code, attackers can easily uncover them using browser inspection tools and gain unauthorized access to backend databases.
Q4: What is client-side logic vulnerability in visual platforms?
It occurs when security checks or administrative restrictions tied to no-code extensions are enforced purely in the browser interface rather than validated securely on the server side, allowing users to bypass them.
Q5: How can development teams secure their modular workflows effectively?
Teams should implement strict plugin vetting processes, conduct routine code audits, avoid outdated repositories, and enforce strict server-side validation and zero-trust principles.